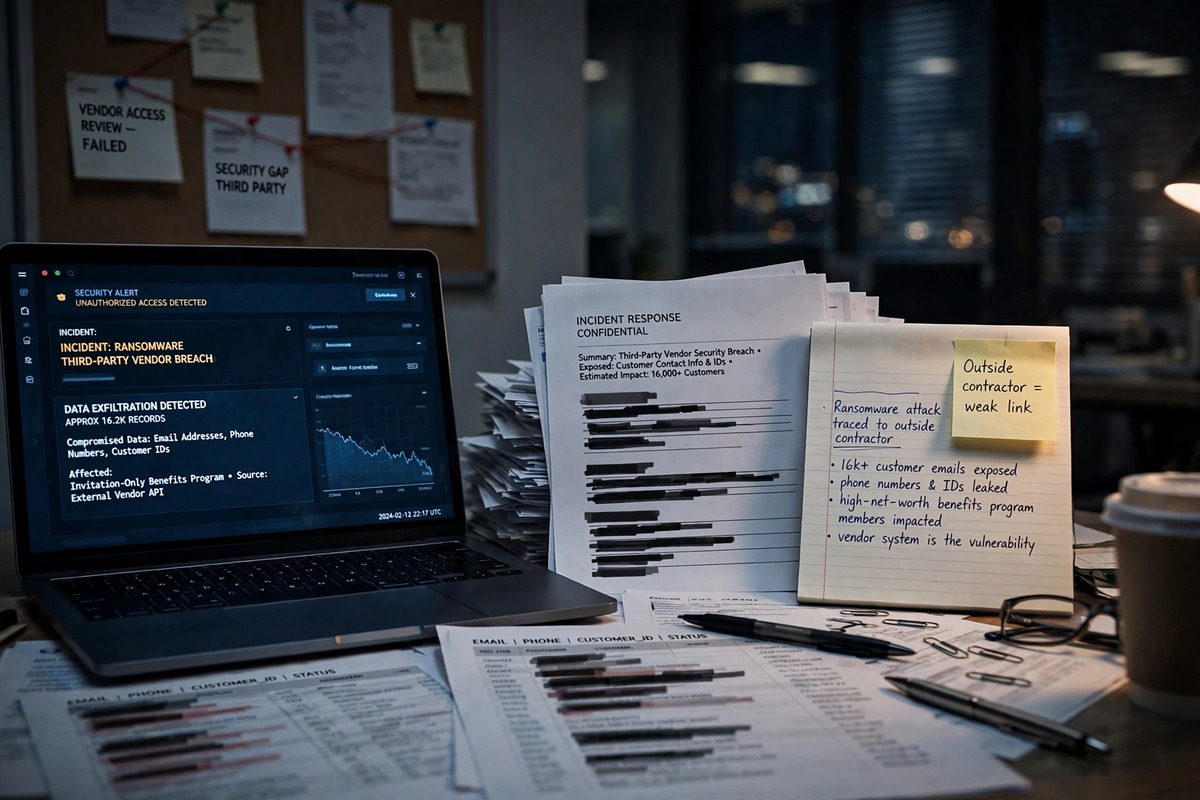

Thousands of customers connected to Visa, Mastercard and JPMorgan Chase reportedly had personal information exposed after a ransomware attack targeted a third-party vendor. The incident is another reminder that a company can spend heavily on security while an outside contractor becomes the unlocked side door. Corporate cybersecurity statements are rarely bedtime reading, but this one may deserve attention.
The exposed information reportedly includes phone numbers, email addresses and customer IDs. Much of the data is tied to wealthy customers enrolled in invitation-only benefit programs. One account cited in the report said more than 16,000 customer emails, some accompanied by phone numbers and account IDs, were connected to a Reserve program for clients with at least $10 million in assets under management.
The narrow silver lining is that credit card numbers do not appear to have been included. Visa said its own systems were not involved and that the incident affected a third-party service provider in the Asia-Pacific region. The company also said no payment data, including card numbers, was affected.
Mastercard described the exposure as a “limited amount of information from a subset of cardholders enrolled in a specific benefit program.” The company said the exposure had been contained, with no effect on its payment network or customers’ ability to use their cards. That may be reassuring, although “limited” is not exactly the word customers want to see attached to their personal information.
JPMorgan Chase said third parties providing services to the firm were targeted. Based on the bank’s investigation, attackers may have accessed marketing data that included customer names and email addresses. Chase also said its customer services were not disrupted. The outside vendor or vendors involved have not been publicly named.
A ransomware group known as n0n has claimed responsibility, according to cybersecurity firm SOCRadar. Reports said the group posted the information online after a 48-hour ransom deadline expired. The companies involved have not confirmed every detail of that claim, but the alleged release has placed the incident squarely in the public eye.
Chase posted this statement: “We have learned that third parties who provide services to the firm were the target of a cyber attack. Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses.”
For customers, the practical concern is not just whether a card number was stolen. Email addresses, phone numbers and account identifiers can still create opportunities for phishing attempts and other scams. Customers connected to the affected programs should remain alert for suspicious messages, especially ones pretending to come from a bank, card company or benefits provider.
The Wall Street Journal was identified as the first outlet to report the incident, according to WLT Report.
🚨 JUST IN: Visa, Mastercard, and JPMorgan Chase have reportedly had their customer data BREACHED, and the hacking group just dumped the files on the internet, per WSJ
Hacking group "n0n" posted the data after its 48-hour ransom deadline ran out
JPMorgan says its outside vendors… pic.twitter.com/Z9DuJHsxYO— Nick Sortor (@nicksortor) November 19, 2026
BREAKING: Cyberattack hits JPMorgan Chase, Visa, and Mastercard, leaking personal data of thousands of customers, per company statements.
More than 16,000 customer emails, some with phone numbers and account IDs, tied to the invitation-only Reserve program for clients with $10M+…
— The Hormuz Letter (@HormuzLetter) November 19, 2026
We have learned that third parties who provide services to the firm were the target of a cyber attack.
Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses.…
— Chase (@Chase) November 19, 2026
Leave a Comment